Short answer: Press Shift+Tab to cycle the mode. Manual (default) asks before every edit and command, acceptEdits lets Claude edit files and run simple file commands without asking, plan lets it read and explore but not edit until you approve a plan, and auto lets it do everything with background safety checks. Set the mode you start in with permissions.defaultMode in ~/.claude/settings.json.
The mode decides how often Claude Code stops to ask you. Too strict, and you press Enter forty times for a refactor. Too loose, and it runs a command you would have stopped. Matching the mode to the job removes most of that friction.
What are the six permission modes?
From Anthropic's documentation, checked against Claude Code 2.1.308:
| Mode | Runs without asking | Best for |
|---|---|---|
default (Manual) | Reads | Reviewing every action, sensitive work |
acceptEdits | Reads, file edits and common file commands (mkdir, touch, mv, cp) | Iterating on code you are reviewing |
plan | Reads, plus commands the safety classifier approves when auto mode is available | Exploring a codebase before changing it |
auto | Everything, with background safety checks | Long tasks, fewer prompts |
dontAsk | Reads in your working folders and pre-approved tools; anything that would ask is denied | Locked-down CI and scripts |
bypassPermissions | Everything | Isolated containers and VMs only |
Your own permission rules still apply in every mode: a deny rule blocks even in bypassPermissions. Claude Code permissions: allow, ask and deny explains the rules.
How do you switch modes?
Press Shift+Tab in the terminal. The cycle runs Manual, then acceptEdits, then plan; auto joins it when auto mode is available to you, and from auto the first press goes back to Manual.
Two modes are never in the cycle unless you start with them:
bypassPermissionsonly appears if you launched with--permission-mode bypassPermissions(or--dangerously-skip-permissions) or set it as your default. You cannot switch into it from a session started without it.dontAsknever appears in the cycle; start with--permission-mode dontAsk.
What does plan mode actually do?
In plan mode Claude reads files, runs shell commands to explore, and writes a plan, but does not edit your source. You then approve the plan (and pick the mode it continues in, so it starts editing), or press Shift+Tab to leave plan mode without approving.
Three ways in: Shift+Tab, /plan in front of a single prompt, or claude --permission-mode plan to start a whole session in it. It is the safest way to let Claude look around a codebase it does not know yet, and the plan doubles as a checklist you can correct before any file changes.
How do you set the mode Claude Code starts in?
In ~/.claude/settings.json:
{
  "permissions": {
    "defaultMode": "acceptEdits"
  }
}Or for one session: claude --permission-mode plan. The flag wins over the setting, and the setting over the built-in default, which is auto for interactive terminal and VS Code sessions from Claude Code 2.1.283 on. The settings value for Manual is default; the installed 2.1.308's --help lists the flag's choice as manual.
One trap: auto and bypassPermissions do nothing when set in a project's .claude/settings.json or .claude/settings.local.json. A repository you clone cannot switch your safety off. Put them in your user settings or use the flag. Claude Code settings: which file wins has the full order.
When is auto mode available?
On all plans, with a supported model: on the Anthropic API, Claude Opus 4.6 or later, Sonnet 4.6 or later, Haiku 5.5 or a Fable model. On Team and Enterprise it is on by default, and administrators can turn it off with permissions.disableAutoMode. Anthropic's own warning: auto mode "reduces permission prompts but does not guarantee safety", so keep reviewing sensitive operations.
When is bypassPermissions safe?
Only where Claude cannot damage anything that matters: a container, a VM or a dev container without internet access. It offers no protection against prompt injection, and on Linux and macOS Claude Code refuses to start in it as root or under sudo unless it detects a recognised sandbox. Administrators can block it entirely with permissions.disableBypassPermissionsMode.
Which mode should you use?
- New codebase, or a change you want to think through: plan.
- Everyday work you review as it happens: acceptEdits.
- A long task you trust the direction of: auto.
- Production configs, secrets, anything you would regret: Manual.
- CI pipelines and scripts: dontAsk with explicit allow rules. Run Claude Code headless in CI shows the setup.
Where can you check this?
Can you set the mode and the rules in one place?
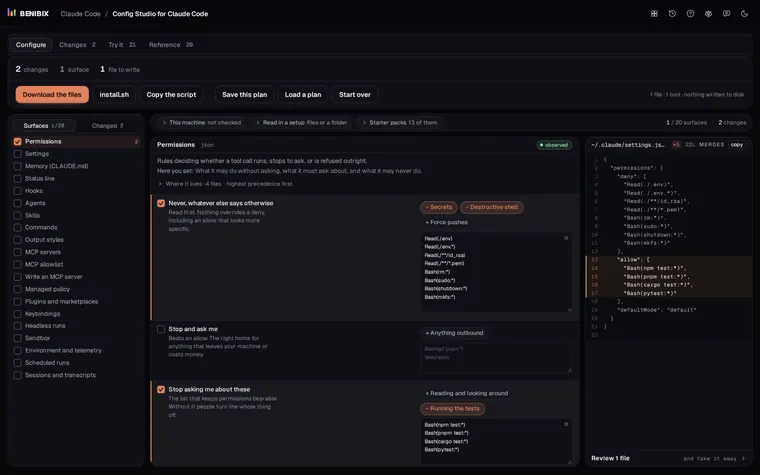
Config Studio for Claude Code explains every file Claude Code reads, including permissions.defaultMode and the allow, ask and deny rules beside it, shows which settings file wins, and writes the settings for you. Nothing changes on your computer until you run its install script yourself.